Free template
Network Security Architecture and Controls Presentation for IT Teams
This network security PPT template helps network engineers brief IT teams on how an environment is protected. The eight-slide deck opens with an Architecture & Controls cover, then shows an illustrative topology in which external and user networks pass through policy enforcement before reaching DMZ and core services. Next come an exposure map for external entry, privileged access and east-west movement, a boundary rule table that ties each allowed flow to a control and evidence, and a session authorization flow that weighs user identity, device context and the requested resource before granting or challenging access. The closing slides turn this cybersecurity presentation into action with a four-step observe, triage, escalate and review handoff, a gap register with priority, owner and due date columns, and a review checklist with approval fields. Values stay as bracketed placeholders, footers carry NIST SP 800-207 reference notes, and the blue-gray layouts with server-rack photography work as PowerPoint slides or through the Google Slides conversion.
Explore Deckgist's AI presentation maker to turn network audit notes or security policy PDFs into a structured, editable briefing deck.
Create a presentation with AI
Enter a topic or upload reference files, then choose a theme to create a new presentation.
Create with a theme
Enter a topic or upload reference files, then choose a theme to create a new presentation.
Supports documents, PDFs, PPTs, and text files
Generate an editable presentation
AI organizes your content and completes the layout
No topic or upload needed
No topic or upload needed
What’s included
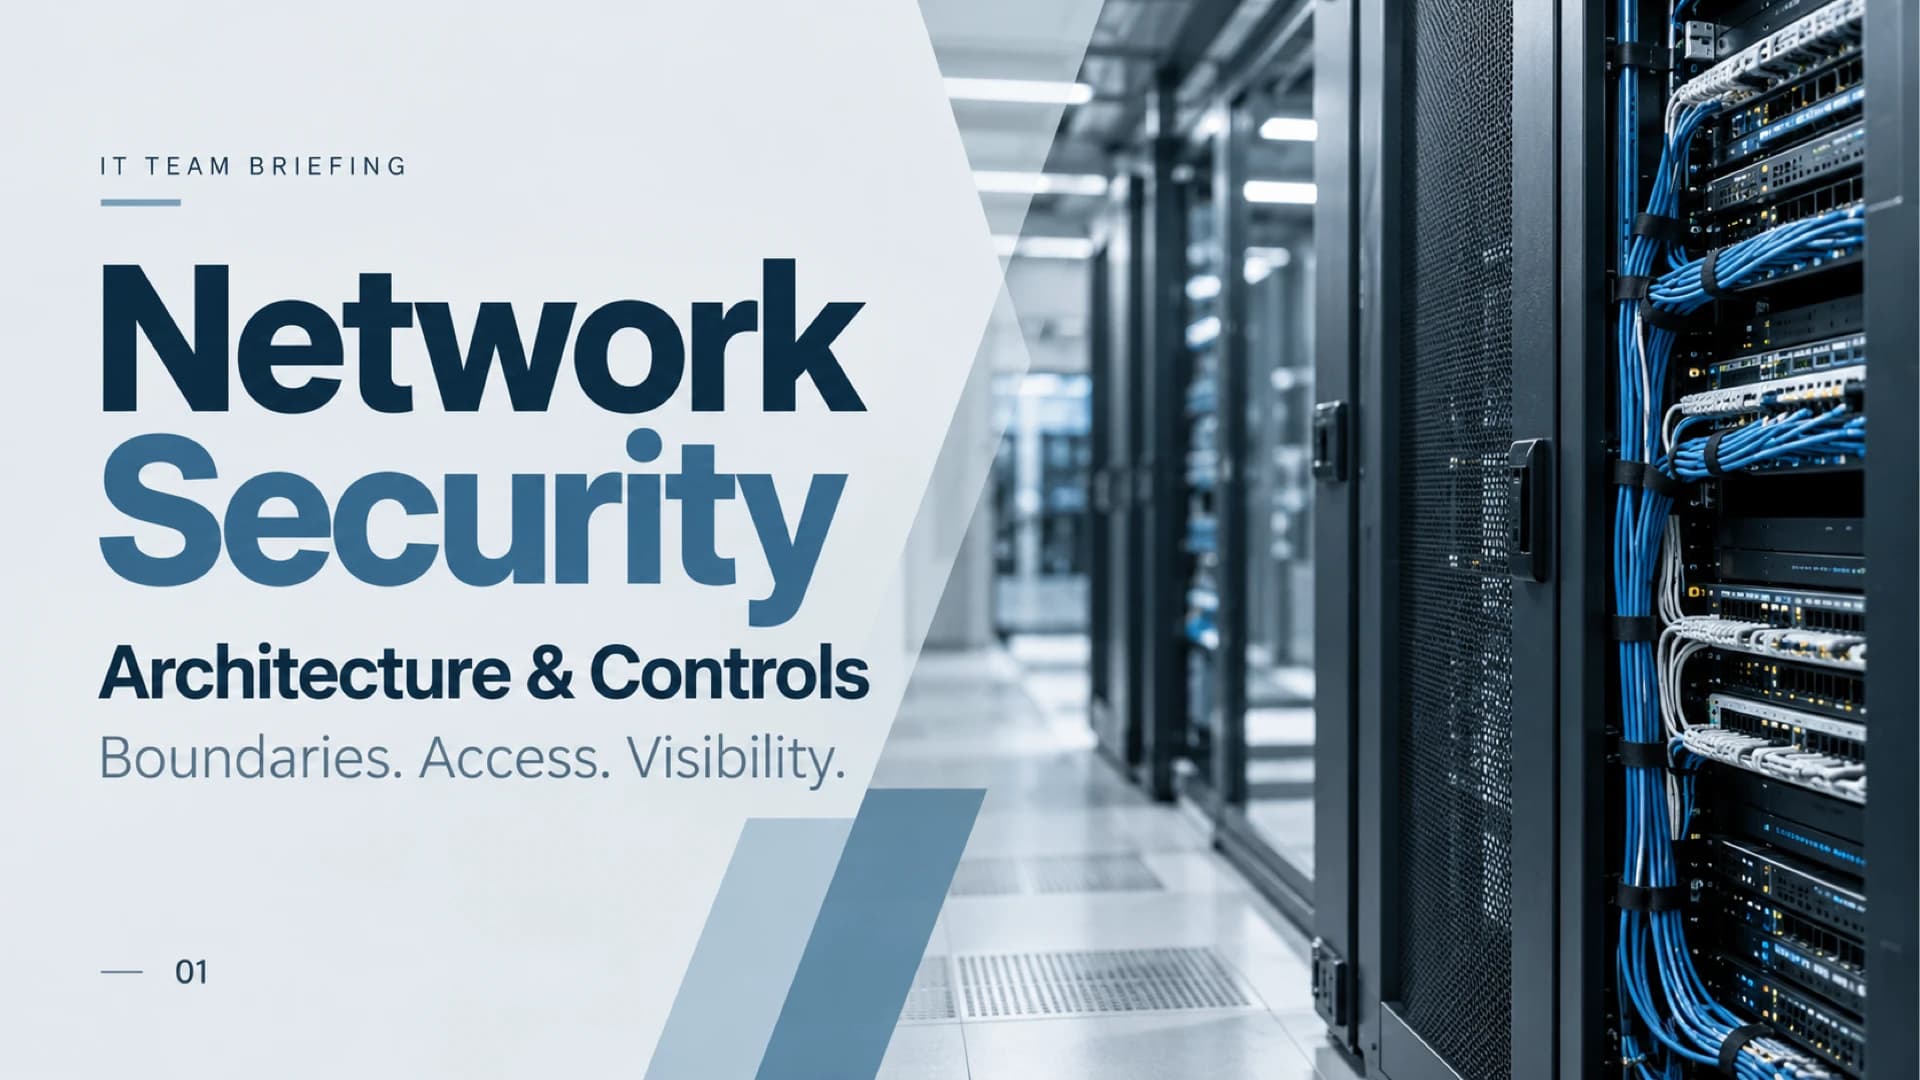
Network security architecture and controls cover
IT team briefing cover titled Network Security: Architecture & Controls with the tagline Boundaries. Access. Visibility.
- • IT team briefing
- • Boundaries. Access. Visibility.
Illustrative network architecture with policy enforcement
Example topology where external and user networks pass through a central policy enforcement layer before reaching DMZ and core services, noting that flows require explicit authorization.
Show full textCollapse
Threat and exposure map
A review table for mapping exposure before choosing controls, covering external entry, privileged access and east-west movement with placeholder asset and evidence fields.
Show full textCollapse
Segmentation and boundary control rules
A boundary rule table that links each source-to-destination flow to its business need, the control to validate and test or log evidence, stressing that network location alone does not grant trust.
Show full textCollapse
Identity, access and secure connections flow
Conceptual flow in which user identity, device context and the requested resource feed a policy decision that results in an authorized session or a deny-or-challenge outcome.
Show full textCollapse
Monitoring and incident escalation handoff
Four numbered steps for turning monitoring into an accountable handoff, with placeholder fields for signal, criteria, contact, action, response target and case record.
Show full textCollapse
Controls gap and priority roadmap
A gap register with priority, owner and due date columns plus an assess, agree, schedule and verify sequence for planning remediation work.
Show full textCollapse
Ownership and review checklist
Closing checklist confirming scope, boundary rules, access policy, monitoring handoff and open gaps, with fields for review owner, next review date and approval.
Show full textCollapse
Best for
- Network security architecture briefing for an IT team
- Network segmentation and boundary rule review
- Identity-based access policy walkthrough
- Security monitoring and incident escalation handoff planning
- Controls gap and remediation priority meeting
Who this template is for
- Network engineers
- IT infrastructure teams
- Security operations analysts
- IT managers
- Information security leads
Features of this template+
- Illustrative topology diagram routing external and user networks through policy enforcement to DMZ and core services
- Four-column placeholder tables for exposure mapping, boundary rules and a prioritized controls gap register
- Session authorization flow from identity, device and resource inputs to an authorized session or a deny-or-challenge outcome
- Numbered observe, triage, escalate and review handoff with response target and case record fields
- Blue-gray data center design with server-rack photography, angled panels and bold two-tone headlines
- Editable 16:9 PowerPoint slides with a Google Slides conversion option and placeholder-only values